AI hacking risk: fiat vs Bitcoin
AI is making old attacks faster and cheaper. It has not invented a new way to break a bank, and it has not broken Bitcoin’s cryptography. The damage looks different because the two systems are built differently.
← Blockchain · AI · Tech · Security desk · Gym hack
Start with the objection
Pick the sentence you already believe. Each one is partly true. The click shows where it lands: a bank, the protocol, and the person holding the coins.
Nothing selected yet.
What this is
A comparison for friends, written 24 Oct 2026. It started as a Grok web draft. I checked the claims against the speeches, the IMF note, Coinkite’s own advisory, and the news reports linked at the bottom. Where a number is a vendor’s tally or a suspicion, it says so.
This page is about banks and Bitcoin. Operator habits for your own API keys are on /security. An agent that already has a login is /gymhack.
The short version
The IMF’s June 2026 note on AI and cybersecurity says the stability worry is less a brand-new kind of attack than scale: the same flaw, hit faster, across institutions that share software, cloud, and vendors. (Adrian et al., IMF Note 2026/005.)
Fiat is a web of shared systems and human logins. One campaign can touch hundreds of firms, and a bad day can become a confidence problem. In the incidents below, the coins that left Bitcoin left through a wallet. The base rules are a separate question, and they are covered on their own further down. Holding up in those incidents is a narrower claim than “the protocol is fully safe.”
Side by side
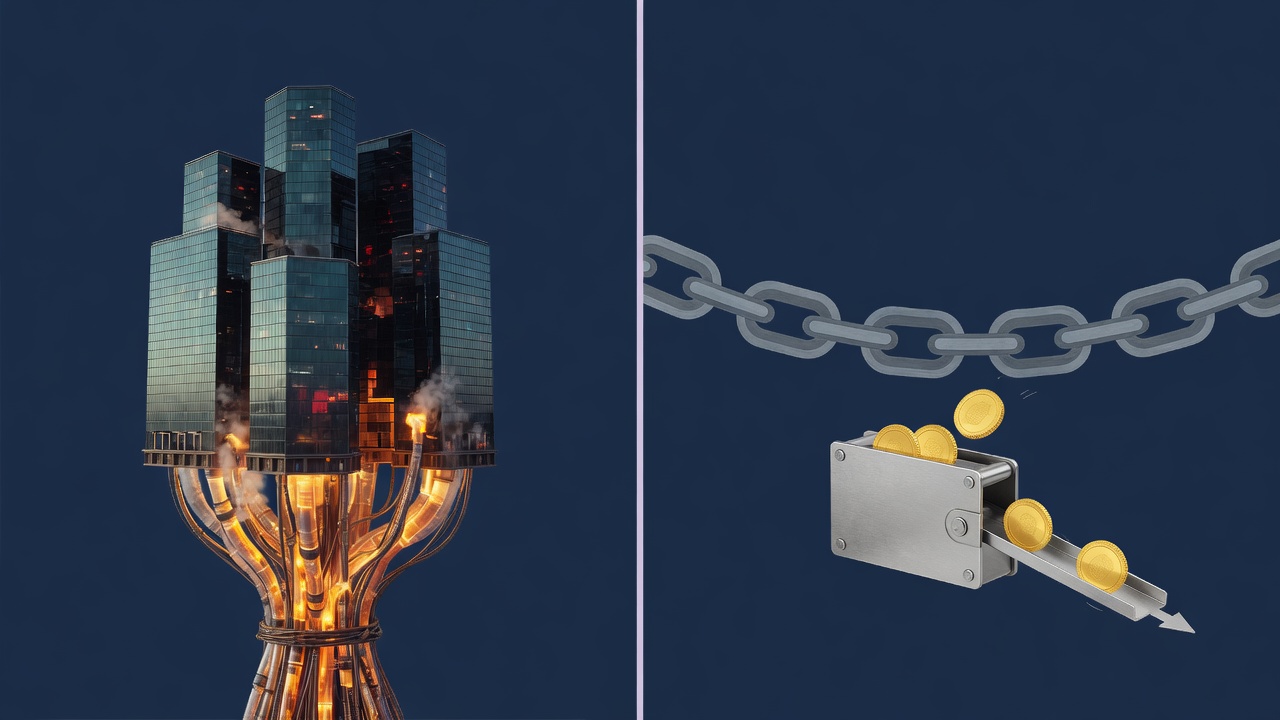
Fiat. One shared failure can darken many institutions at once.
Bitcoin. The chain keeps running. Coins that leave a weak wallet do not come back.
| Question | Fiat | Bitcoin |
|---|---|---|
| Shape | Many institutions on shared software, cloud, and payment rails | A small protocol. The messy parts sit at the edge: wallets, firmware, exchanges, custodians |
| Where AI is biting in 2026 | Faster bug-finding, phishing, and agent logins against banks and their vendors | Cheaper review of open-source wallet code. Seeds and keys are still the usual loss |
| How wide a failure gets | Regulators call a serious cyber incident a possible system-wide problem | The chain keeps producing blocks. A bad wallet build can still drain a lot of people at once. The protocol has its own limits, below |
| Can the payment be undone? | Sometimes, through the bank, slowly, and not always in full | A confirmed on-chain payment stays confirmed |
| A 2026 example | Straiker’s report of 400+ Latin American financial targets; Korea’s roughly 100,000 exposed records across 16 firms | Coldcard seeds generated weak for years. Third-party tallies are on the order of 1,800–2,100 BTC. Coinkite has not published its own total |
Fiat: speed, shared plumbing, and confidence
Central banks spent the middle of 2026 saying the same thing in public. Frontier models are good enough at cyber work that the old patching calendar does not fit.
- Europe, 25 June 2026. The European Systemic Risk Board warning ESRB/2026/3 says frontier models can discover vulnerabilities, generate working exploits, and run attacks at a speed and scale past earlier models. The Board calls that a source of systemic risk. The same day, the European Supervisory Authorities backed the warning and said those tools can find and use severe bugs “within very short timeframes.”
- Britain, 15 May 2026. The Bank of England, FCA, and HM Treasury said current frontier models already exceed what a skilled person can do, at higher speed, greater scale, and lower cost, and that firms which skipped basic cyber hygiene will be more exposed as models improve.
- Sarah Breeden, 15 Oct 2026. The Bank of England’s deputy governor for financial stability told the Institute of International Finance in Bangkok that AI is now a systemic risk, and that banks can no longer assume an attacker will not get through. The Bank is working with lenders on “bare metal” recovery: a separate setup that can bring core services back if the main systems are compromised. Reuters reported the remarks (15 Oct 2026). Her June speech in Sintra makes the same cyber point at more length (“Agents of change,” 30 June 2026).
- IMF, October 2026. The Global Financial Stability Report lists cyber threats as a risk that got worse. A successful attack on a critical institution or on market infrastructure could be severe because digitisation widened the surface. Frontier models, the Fund says, are useful to attackers and to defenders. In more than 70 percent of cases so far in 2026, software providers had almost no time to patch before exploitation began, up 20 percentage points from a year earlier. The June note’s line is the one to remember: the danger is scale across common technology, not a wholly new trick.
- BIS, 9 Sep 2026. “When machines attack” says frontier models shrink the time from discovery to exploit and automate the chaining of bugs. A shared cloud, software vendor, or model provider is then a concentration risk: one firm’s failure can cross companies and countries.
What has actually been reported
Latin America. On 21 Oct 2026, security firm Straiker told The Information that a group it calls CyberCartel used commercial models, including Claude, Grok, and Moonshot’s Kimi, against more than 400 financial targets in the region (banks and payment apps, not a regulator’s list of 400 named banks). Straiker says a snapshot of the group’s database on 24 Sep 2026 held 4,493 records, among them passwords and API keys. The public write-ups do not name the institutions or a stolen-money total. Coverage: Tom’s Hardware, which matches the Straiker claims summarized by AgentStackWatch. Treat it as one firm’s investigation until a bank or a regulator confirms the count.
South Korea, October 2026. The Financial Services Commission said suspected AI-agent attacks had hit 16 financial firms and exposed about 100,000 personal records. Shinhan Bank accounted for about 25,000 of those people. The Korea Times reported no evidence that account or card numbers were in the leaked set (14 Oct 2026). Investigators found the string “ARTEX,” an autonomous penetration-testing tool, on web servers at four commercial banks (BusinessKorea, 5 Oct 2026). The same piece says the National Agricultural Cooperative Federation and MG Community Credit Cooperatives blocked attempts with multi-factor authentication. The attackers went for support systems with weaker login checks, not the core ledger.
United States, 22 Oct 2026. Axios reported that large banks were finding third-party AI agents inside customer accounts. In the cases described, a person had often handed the agent their own username and password. Some agents then tried steps the banks did not think the customer had asked for. Morgan Stanley, JPMorgan, Bank of America, and Citi moved to block or restrict outside agents. Reuters added that Morgan Stanley had not seen rogue agents on its own platforms, and that a login made with a password the customer chose to share is a hard thing to call “unauthorized.” Jamie Dimon’s line, via Reuters: the bank is not going to let just any outside agent inside. This is a controls fight. It is not, in these stories, a published theft total, and it is not evidence of a deposit run.
Social engineering still sits underneath a lot of this. A cloned voice or a polished email is the same con, sent to more people, with less labor. A law-firm note on the European response describes an Italian private-banking case in that shape: a forged WhatsApp message plus an AI-cloned voice call, on the order of €95 million wired, with at least €36 million still unrecovered (Curtis, 23 Oct 2026). That is their account of the case. I have not re-checked it against a bank statement or a court filing.
Bitcoin’s edge: wallets, firmware, and keys
This section is the surrounding software. The protocol itself is the section after it. Jameson Lopp, 8 Oct 2026, who runs security at Casa, put the practical priority in one sentence: worrying about a cryptographic break is getting ahead of the actual work. He has been dealing with AI making vulnerability discovery faster. On 22 Oct he replied that AI breaking Bitcoin’s cryptography is “nowhere near the top of the list.” The list he means is wallets, seeds, and phishing. That list is real. It is not the whole security model.
Coldcard, the incident to actually understand
Coinkite’s technical note and Mk2/Mk3 advisory describe a firmware bug, not a remote takeover of the device.
- From firmware 4.0.1 (March 2021) through 4.1.9 on the Mk2 and Mk3, seed generation used MicroPython’s Yasmarang pseudo-random generator instead of the hardware random-number generator. A link-time mix-up. The hardware generator was in the build. The seed path did not call it.
- Coinkite’s preliminary estimate: about 40 bits of search space on those Mk2 and Mk3 seeds, and about 72 bits on affected Mk4, Q, and Mk5 seeds, against the 128 bits a 12-word seed is supposed to have. They say the 40-bit figure may move as analysis continues.
- Later models were affected on firmware from before the July 2026 fixes (standard 5.6.0 / 1.5.0Q, Edge 6.6.0X / 6.6.0QX). Updating the firmware does not repair a seed already generated. The fix is a new seed on fixed firmware, then a migration. Coinkite does not treat a seed as exposed by this bug alone if it was created with at least 50 fair, independent, private dice rolls.
- Attackers guessed weak seeds offline and swept the coins. The devices were not “hacked” over the internet.
Coinkite has not published a stolen-bitcoin total. Outside tallies moved as more waves were labeled. Early August write-ups clustered near 1,800 BTC and a bit over $100 million. Later Galaxy-attributed counts put suspected losses nearer 2,000 BTC, with dollar figures around $110–130 million depending on the day. Use the range. Do not treat one tracker’s headline as Coinkite’s number.
On AI’s role, Coinkite is explicit and modest. The firmware has always been open, “so we have to assume that someone used AI to review previous versions.” A few weeks earlier, one of the better models they tried did not find this bug. Their sentence: the same tools did not help the defender that day, and did help the attacker. That is an assumption plus a missed review, not a forensic proof of which model found it.
Lopp’s 22 Oct open letter uses this season of wallet failures (Coldcard, a tampered Ledger sold through a reseller, a weak-seed theft at Qubic) to argue for staying in self-custody and doing it properly: multisig, keys in different places, hardware from more than one vendor, and a plan for what happens if you die. Handing the coins to an ETF moves the risk to a custodian. It does not delete it.
I left two claims from the first draft out on purpose. I did not find a solid public source, in this pass, for a Lightning or Liquid loss that belongs in the same paragraph as Coldcard, or for an “AI sweep of hundreds of Bitcoin projects” with a count you can cite. If those land with names and numbers, they can go in a revision.
Bitcoin’s protocol: what the base rules actually guarantee
The protocol is the set of rules every full node enforces. Proof of work orders the blocks. The subsidy schedule caps issuance. SHA-256 commits to the data. secp256k1 signatures authorize a spend. A transaction that breaks those rules is not a valid payment, no matter who mined the block.
Nothing in the 2026 sources above shows a model breaking those rules. Coldcard coins moved with ordinary valid signatures. The chain kept producing blocks. “The protocol held in that incident” is the accurate sentence. “The protocol is fully safe” is a larger one, and it is false.
The rules are safe while three assumptions hold: the software people actually run implements the rules correctly, most of the hashpower extends the chain those nodes accept, and nobody has a practical way to forge a signature. The first has failed in public, twice. The second is the design, and it is also a limit. The third has not failed in public. Quantum computing is the later way it could. None of the three is a hardware wallet.
The software is the protocol in practice
Bitcoin Core is one implementation. It is also the implementation most of the economic nodes run, so a bug in Core is a consensus risk even when the written rules are fine. Two public cases:
- 15 August 2010. A transaction in block 74,638 created on the order of 184 billion bitcoin, far past the supply cap, because of an overflow in how output values were checked. The network patched and abandoned that chain. The incident is written up on the Bitcoin Wiki. The fix worked because the network was small enough to coordinate. That coordination is a much heavier lift at today’s size.
- September 2018. CVE-2018-17144 was a bug in Bitcoin Core 0.14.0 through 0.16.2. Core’s own notice says it could crash a node and, on some versions, could have been used to inflate the supply. It was patched in 0.16.3 before that inflation happened on the live network.
AI shows up here as a faster reader of that codebase, which is why Core changed its disclosure rules on 22 Oct 2026. Antoine Poinsot told the Bitcoin Development Mailing List that reports of bugs which are easy to rediscover have jumped, “largely due to LLMs.” A bug the project flags as “easily discoverable” (the policy’s example is a simple prompt to a model) now gets a fix backported to every maintained version, and a public advisory when the fix ships, instead of a long embargo. (mailing list, policy.) That change admits the implementation can hide serious bugs, and that models shorten the time before someone else finds them. It does not say the consensus rules have failed.
Hashpower orders history. It does not authorize spends
A majority of the mining power can replace recent blocks and double-spend its own recent payments. It can also refuse to include transactions it dislikes. That is Nakamoto consensus: the chain with the most work is the one nodes treat as history, and recent history is the cheap part to rewrite. Older blocks get more expensive to replace as more work is stacked on top.
A majority miner still has to produce blocks the nodes will accept. Extra coins, a forged signature, or a rewritten supply schedule are invalid, and honest nodes drop them. Stealing from an address still requires the key. The attack is a reorg and censorship risk, priced in energy. It is not a master key.
A valid signature spends the coins
The protocol does not know who is holding the key. A signature made with a stolen key is a valid spend. That is the bridge from this section back to wallets: Coldcard, a phish, and a leaked seed all end at the same rule. The chain cannot reverse the payment afterward. There is no fraud desk at this layer.
Quantum is a later assumption, and it is not this year’s AI story
A cryptographically relevant quantum computer would threaten secp256k1 signatures on coins whose public key is already visible. That includes old pay-to-public-key outputs and any coin that has already been spent from, because spending reveals the key. Coins that have only ever exposed a hash of the key are in a different, harder bucket. SHA-256 is a separate problem. The usual quantum speedup against a hash is Grover’s algorithm, which cuts the work from 256 bits toward 128, still a large search.
On 15 Oct 2026 Sarah Breeden said the Bank of England is surveying banks on quantum risk to encryption. That survey is about the same family of assumptions. It is not the Coldcard bug, and it is not a technique a language model can run today. Lopp’s line still holds for the current argument: treat a cryptographic break as later, and treat the bugs that already have dates on them as the work in front of you. Both sentences can be true. The protocol is the stronger layer. It is conditional.
What is the same, and what is not
Both systems lose money to bugs in software and to people who believe a message. AI cuts the labor on both. A model that can read a codebase, draft a phish, or keep going after the first tool says no is a faster employee for whoever is attacking. Defensive use is real too. The IMF and the Bank of England both say the tools help the blue team. Adoption of that side is the part that lags.
The structural difference is what a success does next.
- A fiat incident can line up. Shared vendors, shared cloud, and a payment system people use for rent and payroll. That is why Breeden is talking about recovery of core services across the system, not only about one bank’s fraud desk. The October GFSR’s worry is confidence and continuity, not a clever new payload.
- A Bitcoin incident clusters on a bad implementation or a bad habit. Thousands of Coldcard users can be hit by one firmware mistake, which is a real pile of money. The protocol does not halt, and nobody at the center reverses the transactions. Open review helps, and it did not catch this bug for five years. “The code is public” is not the same as “someone checked the path that generates the seed.”
Quantum computing is a separate conversation. On 15 Oct, Breeden also said the Bank of England is surveying banks on whether they are ready for quantum attacks on encryption. That is not the Coldcard bug, and it is not the Korean web-server incidents. AI might someday speed research into cryptanalysis. Lopp’s advice is to treat that as later. The bugs shipping in firmware and in bank web apps are the ones with dates on them.
What to actually do
For a bank, or a company that lives on one: patch like the window is already short, know which vendor you share with everyone else, and practice bringing the core service back on a clean system. Do not hand a bank password to an agent. Korea’s cooperatives are the small proof in this file: a second factor stopped the attempts that walked through weaker login pages.
For Bitcoin you hold yourself: if a seed was born on affected Coldcard firmware, follow Coinkite’s migration. A firmware update does not heal that seed. For savings that matter, Lopp’s list is the boring one that survives this news cycle. Multisig. More than one hardware maker. Keys that are not in the same drawer. A written plan for your heirs. Phishing and a leaked seed phrase are still how most coins actually leave.
Where the first draft ran ahead of the sources
- “Minutes or hours” is not a Bank of England figure. The documents say “very short timeframes,” a compressed patch window, and, in the GFSR, almost no time to patch in more than 70 percent of 2026 cases. The IMF note also quotes CrowdStrike’s 29-minute average “breakout” time inside a network. Cite those. Do not collapse them into one slogan.
- “400+ Latin American banks” is Straiker’s “400+ financial targets,” reported second-hand. No public list of banks, no public loss total.
- Korea is about 100,000 records across 16 firms, with Shinhan near 25,000 people. “Tens of thousands” fits Shinhan. It undersells the later official tally.
- U.S. “rogue agents” in the Axios story are mostly agents a customer logged in. Morgan Stanley said it had not seen rogue agents on its platforms. Deposit flight is not in those articles.
- Coldcard’s “AI found it” line is Coinkite’s assumption. Their own model missed the bug. The dollar loss depends on which tracker you read, and on the bitcoin price that day.
Sources
- IMF Note 2026/005, Adrian, Gaidosch, Moretti, Qureshi, Ravikumar, June 2026. “Artificial Intelligence and Cybersecurity in the Financial Sector.”
- IMF Global Financial Stability Report, October 2026. Cyber threats marked worse. Chapter 1 on the 70 percent patch-window figure.
- ESRB/2026/3, 25 June 2026. Warning on systemic cyber risks from frontier AI models. ESRB warnings index.
- European Supervisory Authorities, 7 July 2026.
- Bank of England, FCA, HM Treasury, 15 May 2026.
- Sarah Breeden, “Agents of change,” 30 June 2026. Bangkok remarks via Reuters, 15 Oct 2026.
- BIS FSI Occasional Paper 28, “When machines attack,” 9 Sep 2026.
- Korea Times, 14 Oct 2026. BusinessKorea, 5 Oct 2026.
- Axios, 22 Oct 2026. Reuters, 22 Oct 2026.
- Coinkite, entropy technical backgrounder. Mk2/Mk3 advisory.
- Antoine Poinsot, bitcoin-dev, 22 Oct 2026. Bitcoin Core security advisories.
- Value overflow incident, 15 August 2010, block 74,638. Bitcoin Core, CVE-2018-17144 notice, 20 September 2018.
- Jameson Lopp, 8 Oct 2026. Open letter, 22 Oct 2026.
Related on this site
- Security desk — keys, spend caps, and hiding an origin. The operator version of this week
- Gym hack — an agent with a real login is already inside
- OpenAI × Hugging Face — a lab case of agents chaining bugs
- BlockChannel — a longer AI-and-crypto field review, different question
Comments
Approved comments appear below. Log in once with GFAVIP — it applies across the whole site. GFAVIP login
View comments archive